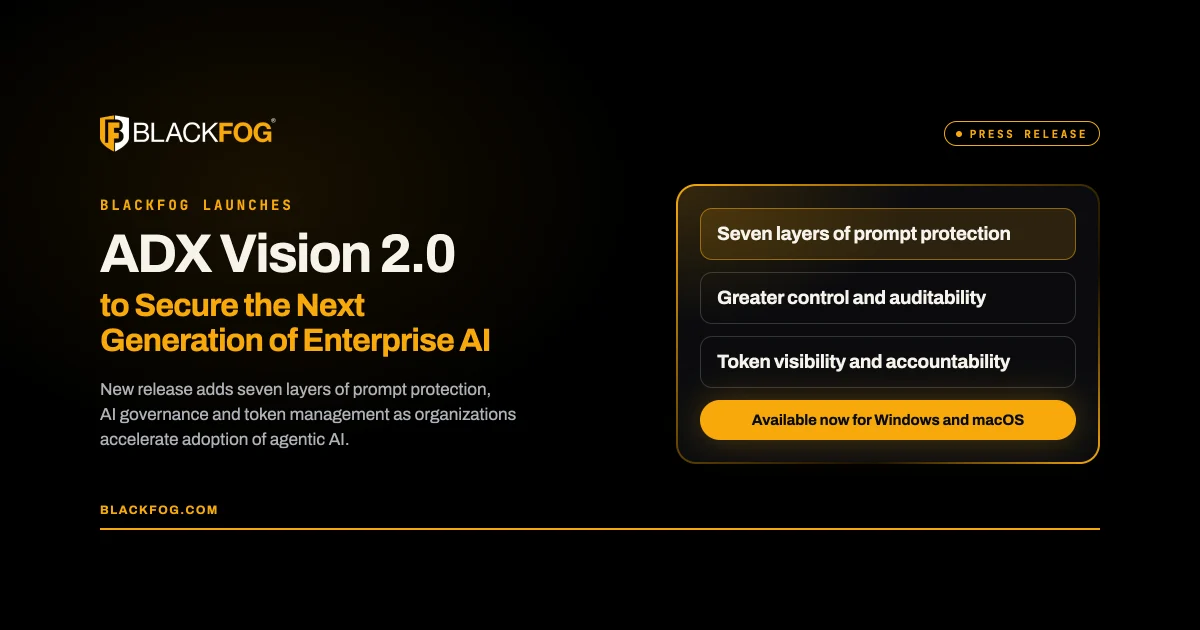
SAN FRANCISCO – September 30, 2026 – BlackFog, a pioneer in anti data exfiltration (ADX), today announced the launch of ADX Vision 2.0, expanding its AI security capabilities to help organizations govern and control the rapidly evolving use of generative and agentic AI across the enterprise.
As employees move from simply interacting with AI tools to deploying agents capable of making decisions and acting on corporate data, the security challenge for organizations is changing. Traditional controls were not designed to address risks such as prompt injection, unauthorized data exposure and limited visibility into what AI is doing with corporate data.
ADX Vision 2.0 provides an independent control layer for enterprise AI that operates directly on the endpoint, before data ever reaches an AI service. This gives organizations visibility, governance and auditability across every AI interaction, whether initiated by an employee or an AI agent, and determines what AI is allowed to do with data, regardless of which tool or model is being used.
The launch builds on ADX Vision’s Shadow AI discovery and control capabilities, expanding into a broader security and governance layer as organizations deploy increasingly autonomous AI systems.
Seven layers of prompt protection
ADX Vision 2.0 introduces seven layers of protection designed to identify prompt injection attempts and other malicious or manipulated prompts:
- Context switching protection
- Obfuscation protection
- Jailbreak detection
- Data exfiltration protection
- Dangerous prompt pattern detection
- Fuzzy keyword detection
- Structural anomaly detection
The same protections apply whether a prompt is written by an employee or generated by an AI agent acting on their behalf. This extends security to autonomous workflows where there is no human oversight of what is being sent.
Custom controls can also be applied at a company or departmental level to identify sensitive information, including credit card numbers, Social Security numbers and domain-specific terminology.
Greater control and auditability
ADX Vision 2.0 enables organizations to redirect AI requests to sanctioned, officially licensed LLM services, helping enforce AI policies without preventing employees from benefiting from the technology. For example, an employee who opens a personal ChatGPT account can be automatically routed to the company’s enterprise AI instance, keeping corporate data within approved environments.
The platform also introduces an optional prompt auditing feature for leading frontier LLMs. This provides greater visibility and accountability around the information being shared with AI systems and supports governance and compliance requirements as regulation evolves.
“AI is quickly moving from something employees interact with to something that can make decisions and take action on their behalf,” said Dr. Darren Williams, founder and CEO of BlackFog. “That changes the security equation. When an agent is sending prompts on an employee’s behalf, there’s no human in the loop to catch a manipulated instruction or a leak of sensitive data. ADX Vision 2.0 inspects agentic prompts with the same protections as those written by humans.”
Token visibility and accountability
ADX Vision 2.0 also introduces a unified view of token consumption across LLMs, showing organizations where tokens are being consumed and by whom. This supports financial planning and drives cost efficiency, while also helping identify potential token theft, where attackers use stolen API keys or credentials to access AI services and run up usage at the organization’s expense.
ADX Vision 2.0 is available now for Windows and macOS. To learn more, visit www.blackfog.com/adx-vision/.